FBI pins record $6.3B Binance heist on North Korean Lazarus Group
The FBI officially attributes the massive theft to TraderTraitor, a notorious hacking ring linked to Pyongyang's Lazarus Group.
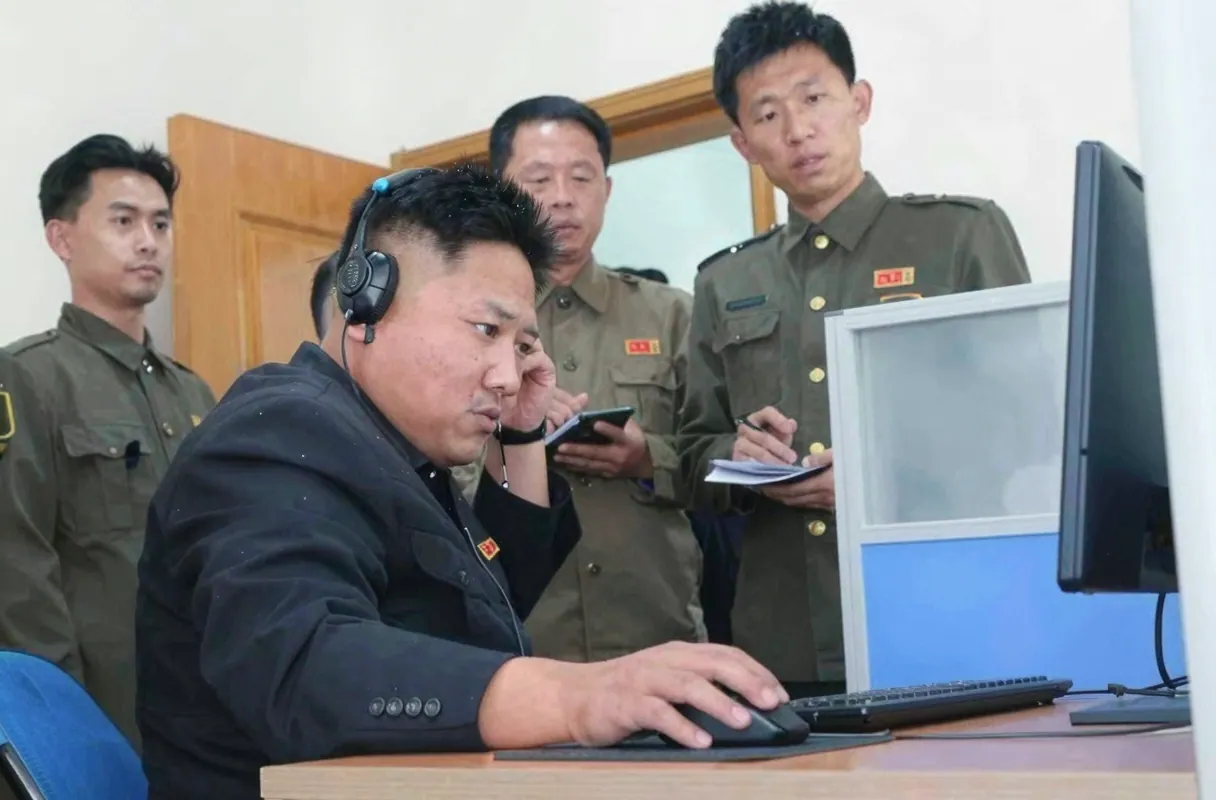
The Federal Bureau of Investigation has formally blamed North Korean hackers for stealing approximately $6.3 billion from cryptocurrency exchange Binance in one of history's largest cyberattacks. In an alert published on Saturday, the agency identified "TraderTraitor," a specific operation within the Lazarus Group, as responsible for the October 29 breach that left the exchange scrambling to recover funds and reassure its customer base.
The Attribution and Immediate Aftermath
While the FBI provided the official confirmation, blockchain intelligence firms had already linked the theft to North Korea prior to the intervention. TRM Labs reported that most of the $6.36 billion haul vanished in roughly 20 minutes TRM Labs. Meanwhile, Elliptic estimated the total closer to $6.43 billion and verified that $2.85 billion of the stolen assets have since been frozen or seized Elliptic.
According to investigators, the hackers are actively swapping their loot for Ethereum to complicate tracking efforts by moving funds through decentralized finance platforms and instant swap services. The FBI has released a list of compromised wallet addresses and is urging exchanges and blockchain analytics firms globally to block any transactions involving these stolen assets.
How the Breach Occurred
The attack originated from internal negligence rather than external intrusion into Binance's core systems. A compromised laptop belonging to a DevOps engineer provided intruders with access to a service container, which allowed them to authorize withdrawals they had no legitimate claim to make According to the exchange.
Following the incident, Binance suspended withdrawals and has since resumed them in phases. The exchange states it has replenished about 95 percent of the stolen assets using its own reserves and emergency funds, with co-CEO Richard Teng promising that customers will not be left to foot the bill Binance. However, replacing the remaining tokens is proving difficult due to their limited liquidity in the market.
A Pattern of North Korean Aggression
The Lazarus Group has a history of targeting cryptocurrency exchanges with sophisticated social engineering and technical exploits. Previous operations include a 2024 attack on Japan's DMM Bitcoin exchange that resulted in $308 million being stolen DMM Bitcoin exchange. The group has previously utilized fake job offers and recruitment exercises to trick employees into handing over system access credentials.
This latest incident follows a similar pattern recently confirmed by other exchanges. Crypto platform Bitget also attributed a $387.5 million wallet raid to North Korean hackers, with its CEO noting that "IP behavioral patterns and on-chain signatures" point to Kim's cronies Bitget. Binance is not facing this level of financial loss for the first time; in 2022, attackers exploited a bridge vulnerability on its BNB blockchain to steal roughly $566 million Binance bridge hack.
Despite Binance's financial commitment to its users, the exchange has seen significant outflows as customers seek alternative platforms. Approximately $3.64 billion in net withdrawals were recorded after services resumed, representing about 2.1 percent of the company's reported assets Binance net outflows. While the exchange may have the liquidity to make customers whole, investigators face a formidable challenge in tracking billions of dollars as the North Korean hackers attempt to launder the funds beyond their reach.